CMMC 2.0 vs. CMMC 1.0: The Complete Compliance Path for Defense Contractors

CMMC 2.0: Key Takeaways
- CMMC 2.0 replaces the five maturity levels in CMMC 1.0 with three and aligns Level 2 directly with the 110 security requirements in NIST SP 800-171 Rev. 2.
- Level 1 protects Federal Contract Information (FCI) and includes 15 security requirements based on FAR 52.204-21. The DoD estimates it applies to approximately 63% of the Defense Industrial Base.
- CMMC Level 2 applies to systems that process, store, or transmit Controlled Unclassified Information (CUI) and requires organizations within the assessment scope to implement the 110 security requirements in NIST SP 800-171 Rev. 2.
- On July 13, 2026, the Department suspended the Phase 2 requirements that had been scheduled to take effect on November 10, 2026, while it reviews and reforms the program. Phase 1 self-assessment requirements remain in effect.
- Organizations subject to applicable CMMC and DFARs requiements must continue maintaining required SPRS records and annual affirmations. Knowingly false statements about cybersecurity compliance can create False Claims Act exposure.
- Limiting CUI to a dedicated enclave can significantly reduce the cost and scope of a CMMC 2.0 assessment.
Two numbers define the biggest change between CMMC 1.0 and CMMC 2.0: 15 and 110.
Organizations that handle only Federal Contract Information (FCI) must meet 15 security requirements under CMMC Level 1. Those that process, store, or transmit Controlled Unclassified Information (CUI) must implement 110 security requirements under CMMC 2.0.
The difference between those two levels can mean the difference between a relatively straightforward self-assessment and a significantly larger compliance investment.
Choosing the wrong level can lead to unnecessary costs or leave your organization unprepared for contract requirements.
The DoD estimated that roughly 80,000 organizations would fall into the 110-control tier.
Yet, as of the October 2025 CyberAB Town Hall, only 431 organizations had achieved certification.
For most defense contractors, determining the right path starts with a single question: Does your organization handle Controlled Unclassified Information?
How Is CMMC 2.0 Different From CMMC 1.0?
CMMC 2.0 simplifies the original framework by reducing the certification model from five levels to three, removing the maturity-process requirements, and aligning Level 2 directly with NIST SP 800-171 Rev. 2.
That alignment is the biggest change.
Contractors handling Controlled Unclassified Information (CUI) were already required to implement NIST SP 800-171 under DFARS 252.204-7012.
Rather than introducing a new cybersecurity standard, CMMC 2.0 verifies compliance with security requirements that many organizations were already expected to meet.
The assessment model also changed. Level 1 organizations complete annual self-assessments, while Level 2 organizations either perform a self-assessment or undergo certification by a Certified Third-Party Assessment Organization (C3PAO), depending on the sensitivity of the contract.
As a general rule, systems that process, store, or transmit only FCI fall under Level 1, while systems handling CUI generally fall under Level 2. The solicitation or contract identifies the CMMC status required for the award.
Although the Department of Defense paused the planned Phase 2 rollout in July 2026, the underlying security obligations remain in force.
Contractors must still comply with NIST SP 800-171, meet applicable DFARS requirements, and submit annual affirmations through the Supplier Performance Risk System (SPRS) where required.
How Do CMMC Level 1 and Level 2 Differ on Scope, Cost, and Timeline?
Level 1 focuses on fundamental cybersecurity safeguards. Level 2 requires a comprehensive security program aligned with NIST SP 800-171.
| Level 1 (Foundational) | Level 2 (Advanced) | |
| Protects | Federal Contract Information (FCI) | Controlled Unclassified Information (CUI) |
| Requirements | 15, from FAR 52.204-21 | 110, from NIST SP 800-171 Rev 2 |
| Assessment | Annual self-assessment plus SPRS affirmation | Self or C3PAO, triennial, with annual affirmation |
| Status during the pause | In effect under Phase 1 | Level 2 (Self) may be required; C3PAO requirement suspended |
| Typical readiness and assessment investment* | $5,000 to $20,000 | $50,000 to $150,000+ in year one |
| Timeline | Weeks | 6 to 14 months |
| Share of DIB | ~63% (DoD estimate) | ~80,000 organizations (DoD estimate) |
It’s also worth clearing up a common myth: CMMC Level 1 includes 15 security requirements, not 17.
Early DoD self-assessment guidance referenced 17 requirements, but three Physical Protection requirements were later consolidated into a single requirement.
The final rule in 32 CFR 170.14 now references the 15 safeguards in FAR 52.204-21(b)(1)(i) through (xv). Many online guides still reflect the earlier version.
For CMMC 2.0, the largest compliance costs typically come before the assessment.
Developing a System Security Plan (SSP), documenting a Plan of Action and Milestones (POA&M), collecting evidence for all 110 NIST SP 800-171 security requirements, and remediating identified gaps usually account for most of the project budget.
The assessment itself is often only one component of the total investment.
The same is true of the timeline. Organizations with mature security controls and documented processes can often achieve CMMC 2.0 readiness in about six months.
Those starting with limited documentation or significant control gaps frequently require a year or longer to prepare.
Do You Need CMMC Level 2? A Quick Self-Check
One question usually determines the answer: Does your organization process, store, or transmit Controlled Unclassified Information (CUI)?
If the answer is yes, the systems that handle that information will generally need to meet CMMC 2.0 requirements. If the systems used for contract performance handle only FCI, Level 1 will generally be the applicable CMMC requirement. Confirm the required status in the solicitation or contract.
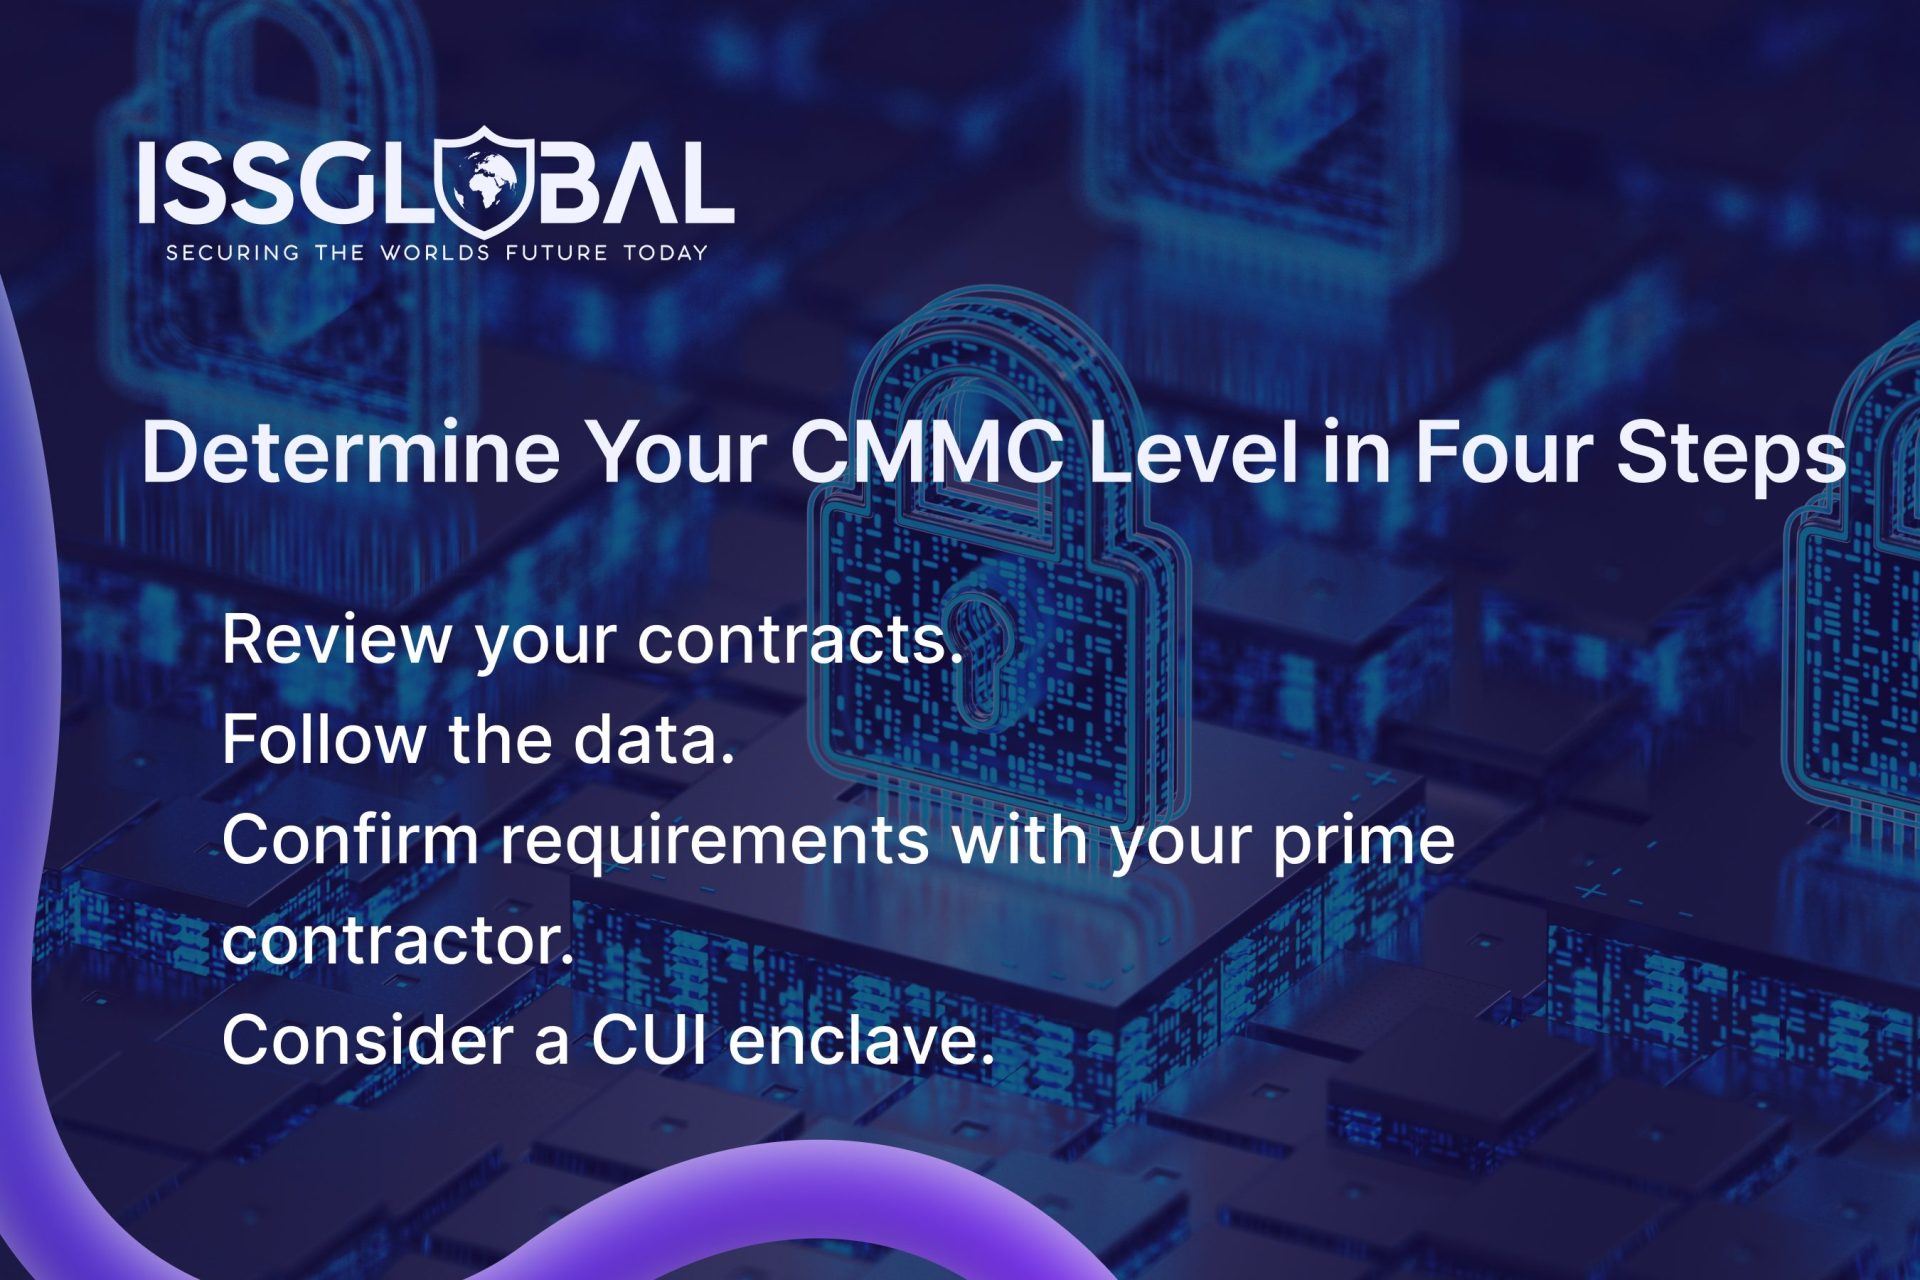
Use these four checks to determine where you stand:
1. Review your contracts.
Don’t rely on assumptions. The presence of DFARS 252.204-7012 often indicates that CUI protection requirements apply. You should also look for CUI markings on drawings, specifications, technical data, and other information provided by the Department of Defense or a prime contractor.
2. Follow the data.
CUI doesn’t always stay where you expect it. It can be stored in shared drives, engineering workstations, email systems, cloud collaboration platforms, CRM applications, or file-sharing services. Understanding where the data resides is essential for accurately defining your CMMC assessment scope.
3. Confirm requirements with your prime contractor.
CMMC 2.0 obligations flow through the defense supply chain. If you’re unsure whether your contracts involve CUI, ask the prime contractor which information and CMMC requirements are being flowed down, but verify the location and handling of CUI within your own environment before defining the assessment boundary.
4. Consider a CUI enclave.
A properly designed CUI enclave may reduce the assessment boundary, although connected systems, security protection assets, administrative services, and external providers may remain in scope.
A smaller assessment boundary often translates into lower implementation costs and a more manageable certification effort.
Many organizations discover that CUI exists in more systems than they initially expected.
That’s why defining the assessment boundary should come before estimating costs or planning remediation.
Our Cybersecurity Strategic Management team helps organizations identify where CUI resides, establish the appropriate assessment scope, and develop a practical roadmap to CMMC compliance.
Why Do Contractors Need Outside Expertise for CMMC?
CMMC readiness requires more than implementing security controls.
Organizations must interpret federal requirements, remediate technical gaps, and produce the evidence an assessor expects.
The challenge is reflected in numbers. As of October 2025, only 431 organizations had achieved final Level 2 certification, despite DoD estimates that roughly 80,000 organizations would eventually require it.
A CyberSheath report published the same month found that only 1% of Defense Industrial Base organizations considered themselves fully prepared, while fewer than half had completed foundational documentation such as a System Security Plan (SSP) or Plan of Action and Milestones (POA&M).
Documentation is often where organizations fall short. A control may be implemented correctly, but without evidence that it operates consistently, an assessor cannot verify compliance.
A structured gap assessment identifies technical, documentation, and process gaps before a formal assessment, helping organizations focus remediation efforts and prepare with greater confidence.
How Does the 7-Layer Staffing Model Support CMMC Readiness?
Preparing for CMMC 2.0 requires a mix of compliance expertise, security engineering, and technical documentation.
Most contractors don’t need those skills full time, but they do need them at the right stages of the project.
Our 7-Layer Staffing model extends your team with specialists who scale to your needs. Additional resources can be brought in during assessment, remediation, and documentation, then reduced as your compliance program moves into ongoing operations.
Maintaining CMMC readiness is an ongoing effort.
Level 2 certifications remain valid for three years, annual SPRS affirmations are still required, and evidence must be collected continuously.
ISS365 supports continuous monitoring and evidence collection, helping organizations stay audit-ready between assessments.
How Can You Prepare for a Level 2 Assessment Without Derailing Development?
The key is to integrate CMMC preparation into existing projects instead of pausing delivery. Organizations that stop business operations to focus solely on compliance often create unnecessary delays and costs.
1. Define Your CUI Boundary
Identify the systems that process, store, or transmit Controlled Unclassified Information (CUI). A well-defined assessment scope reduces both the cost and complexity of Level 2 compliance.
2. Assess Your Current Readiness
Evaluate your environment against all 110 NIST SP 800-171 security requirements and establish an accurate SPRS score. This provides a clear starting point for remediation.
3. Prioritize Documentation and Remediation
Develop or update the System Security Plan (SSP), document remaining deficiencies in an authorized Plan of Action and Milestones (POA&M) where permitted, and remediate technical gaps.
4. Implement Improvements in Phases
Address the highest-priority security gaps first and align remediation with your normal release schedule instead of halting development.
5. Maintain Compliance
Validate your evidence, keep your SPRS affirmation accurate, and monitor controls continuously so you’re prepared for future assessments.
A phased approach can help organizations strengthen their cybersecurity posture while maintaining delivery schedules and supporting ongoing contract commitments.
Why Do Defense Contractors Choose ISSGlobal for CMMC Readiness?
CMMC requires organizations to balance technical security with regulatory compliance. Focusing on one without the other often leads to delays, additional remediation, or assessment findings.
We bring both disciplines together. We help contractors define CUI boundaries, assess environments against the 110 NIST SP 800-171 security requirements, develop assessment-ready documentation, remediate security gaps, and maintain continuous compliance through ISS365.
Our advisory-led, technology-agnostic approach is built around your environment, not a specific product or platform. Because we also support frameworks such as NIST SP 800-171, SOC 2, FedRAMP, and PCI DSS, we help organizations build a compliance program that scales across multiple customer and regulatory requirements.
As CMMC continues to evolve, we provide practical guidance based on the current requirements, helping defense contractors prepare with confidence while maintaining business operations.
Which CMMC Path Applies: 15 Requirements or 110?
The numbers matter, but scope determines how broadly the 110 Level 2 requirements apply across your environment.
Contractors who scope carefully often find the 110-control tier applies to a narrower slice of their environment than they feared. A properly scoped enclave can sometimes reduce Level 2 cost substantially compared with placing the entire enterprise environment in scope.
Contractors who postpone scoping often discover the true assessment boundary only after remediation has begun, when expanding the scope3 becomes significantly more expensive.
Fifteen or 110 is a question with a real answer. Getting it wrong in either direction costs money, and getting it wrong upward costs the most.
Frequently Asked Questions About CMMC 2.0 and Compliance Levels
Short answers to what defense contractors ask us most.
1. Do I need CMMC Level 1 or Level 2?
In general, organizations handling CUI require Level 2, while those handling only FCI typically require Level 1. Your solicitation or contract specifies the required CMMC status.
2. How much does CMMC 2.0 readiness and assessment cost?
Roughly $5,000 to $20,000 for Level 1, and $50,000 to $150,000 or more in year one for Level 2. Scope drives the range more than company size does.
3. What changed from CMMC 1.0 to CMMC 2.0?
Five levels became three, the maturity-process requirements were removed, Level 2 was aligned to NIST SP 800-171 Rev 2, and self-assessment was permitted at Level 1 and for some Level 2 contracts.
4. Is CMMC still required after the Phase 2 pause?
Yes. Phase 1 requirements remain in effect. Contractors subject to applicable CMMC and DFARS clauses must continue maintaining required self-assessments, SPRS records, and annual affirmations of continuous compliance.
5. How many controls are in CMMC Level 1?
Fifteen, from FAR 52.204-21. Guides citing 17 haven’t caught up with the consolidation of three Physical Protection requirements into one.